
Table 1:
Summary of key findings and research gaps in prior studies
| Study | Key findings | Research gaps |
|---|---|---|
| Kwon et al. [3] | Classified password-cracking methods into dictionary attacks, brute-force attacks, and hybrid approaches. Highlighted the effectiveness of optimized dictionaries. | Did not explore countermeasures in-depth or propose improved password security strategies. |
| Florêncio and Herley [1] | Found that complexity requirements in password policies often lead to predictable patterns. | Lacked experimental validation of alternative password creation strategies. |
| Toubiana et al. [10] | Demonstrated that user psychology plays a crucial role in password security and retention. | Did not propose concrete solutions to balance usability and security. |
| Bonneau et al. [11] | Reviewed alternative authentication methods like biometrics and hardware tokens. Found limitations in spoofability and hardware failure risks. | Did not address how these alternatives compare in real-world adoption. |
| Wang and Zhang [12] | Found that password managers improve security but also pose risks if compromised. | Did not analyze specific attack vectors against password managers. |
| Liu et al. [2] | Developed a machine learning model for predicting password strength, improving accuracy over traditional heuristics. | Did not implement real-world usability testing for their model. |
| Wu et al. [5] | Showed that cybersecurity training improves password security awareness and user behavior. | Did not measure long-term retention of learned security habits. |
| Hadnagy [13] | Analyzed social engineering attacks and their role in password security breaches. | Did not propose effective large-scale mitigation techniques. |
| Miller et al. [4] | Compared efficiency of password-cracking tools (e.g., Hashcat and John the Ripper). | Lacked evaluation of emerging AI-powered password-cracking methods. |
| Das et al. [7] | Investigated rainbow table attacks and emphasized salting as an effective countermeasure. | Did not explore advanced alternatives such as memory-hard hashing functions. |
| McCarty and Leach [16] | Explored MFA as a supplement to passwords. Found usability challenges limiting adoption. | Did not propose strategies for improving MFA usability. |
| Zhang et al. [18] | Developed a deep learning model to predict weak passwords with high accuracy. | Lacked analysis on defenses against AI-driven password attacks. |
| Wu et al. [5] | Demonstrated that longer passwords significantly reduce cracking success rates. | Did not evaluate the usability trade-offs of very long passphrases. |
| Ruoti and Muir [9] | Studied password reuse across multiple sites and found that reuse increases vulnerability. | Did not propose large-scale mitigation strategies for password reuse. |
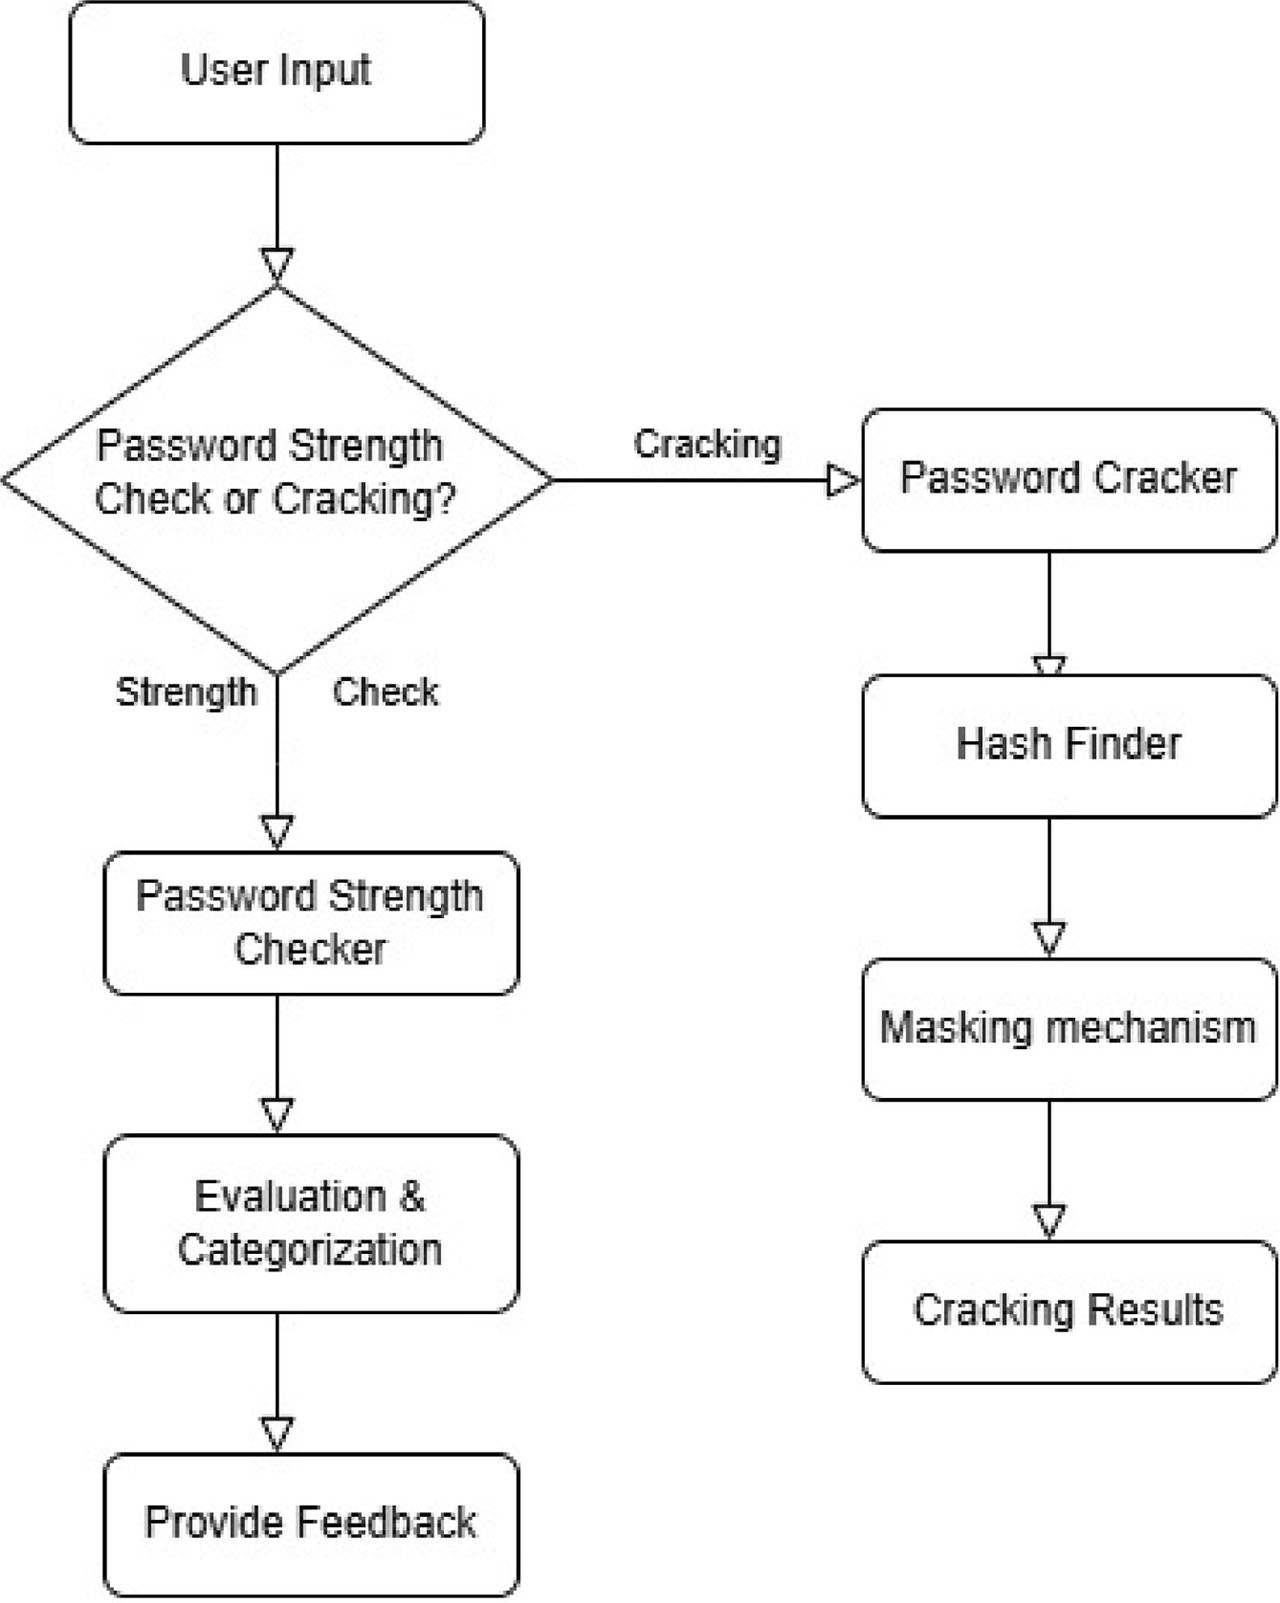
Figure 1:
PassCrack system architecture that illustrates password strength evaluation and cracking workflow.
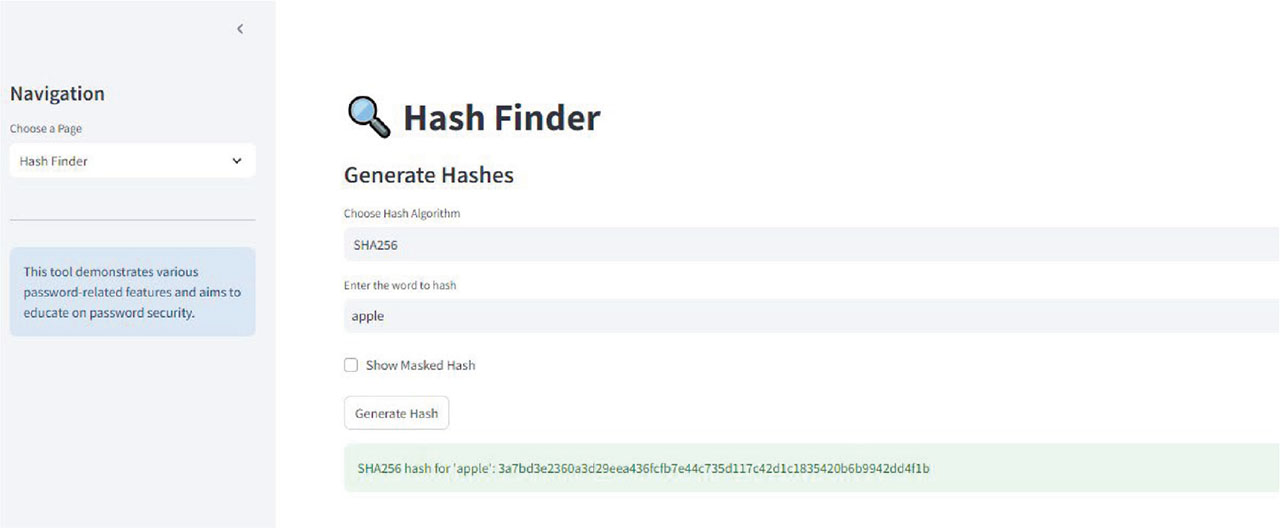
Figure 2:
Hash Finder. Example of SHA256 hash generation for the word “apple.”
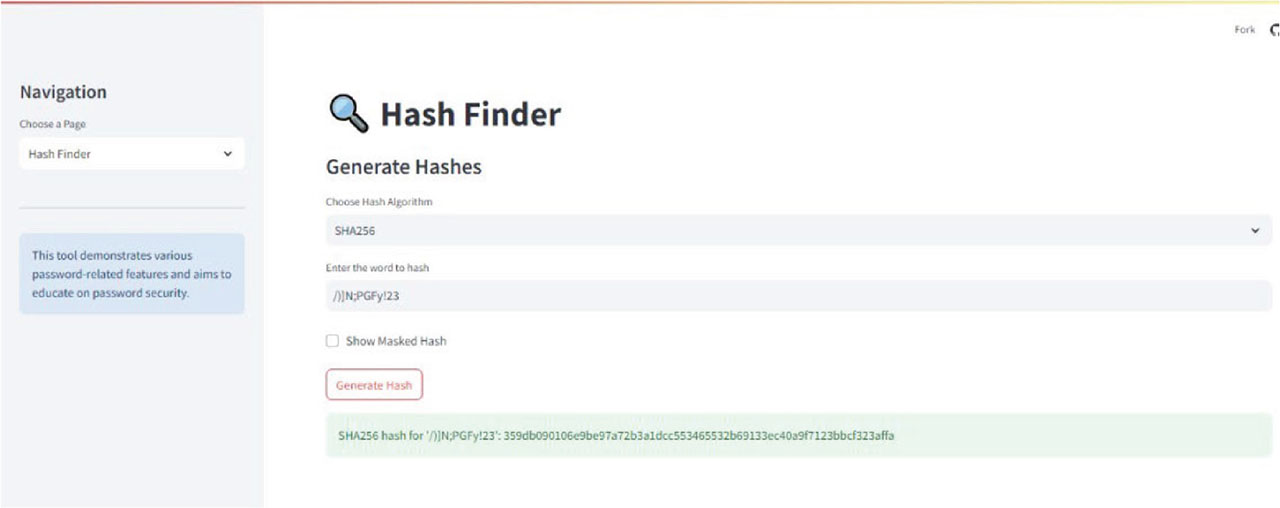
Figure 3:
Hash Finder. Example of SHA256 hash generation for the word “/)]N;PGFy!23.”
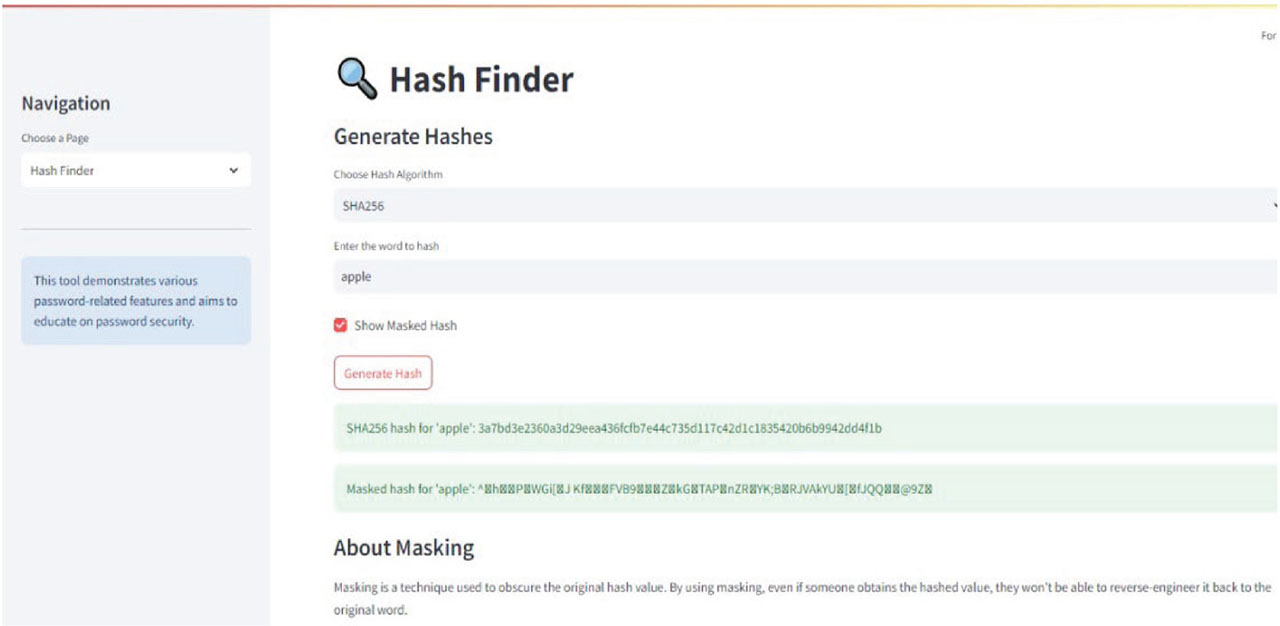
Figure 4:
Masked hash of the word “apple” using SHA256.
Table 2:
Scoring rubric for password strength
| Criteria | Weak (<40%) | Moderate (40%–70%) | Strong (>70%) |
|---|---|---|---|
| Length | <8 characters | 8–12 characters | >12 characters |
| Character variety | Only letters or numbers | Mix of letters and numbers | Uppercase and lowercase letters, numbers, and symbols |
| Pattern complexity | Common words, predictable | Partial randomness, slight patterns | No patterns, highly randomized |
| Entropy score | Low (<40 bits) | Medium (40–70 bits) | High (>70 bits) |
| Resistance to attacks | Vulnerable to brute-force, dictionary attacks | Moderate resistance | Highly resistant to attacks |
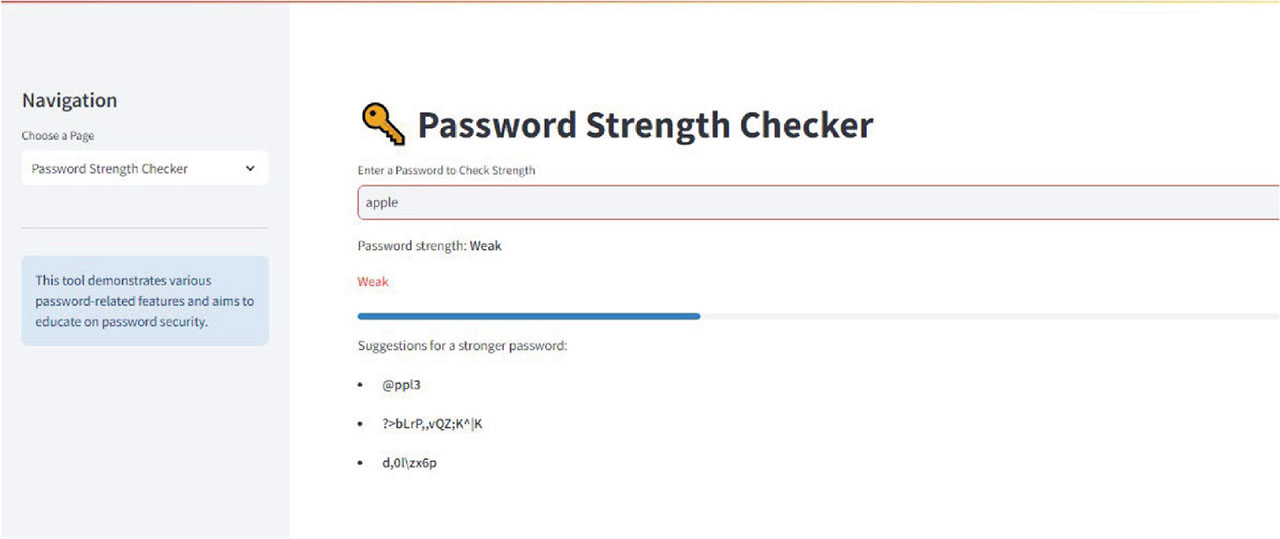
Figure 5:
Testing the strength of the word “apple” as a password.
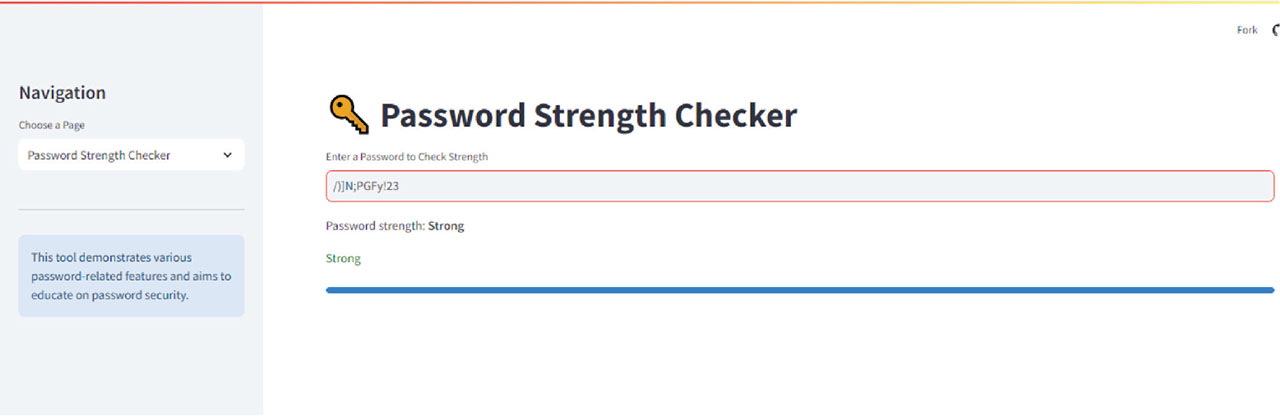
Figure 6:
Testing the strength of the stronger password recommendations.
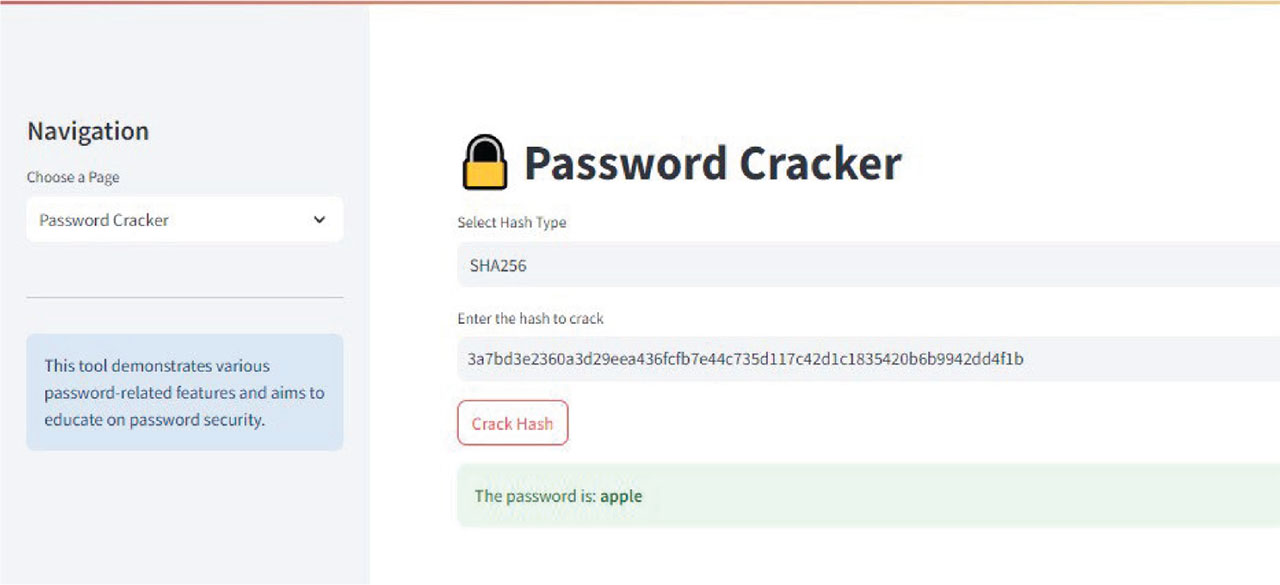
Figure 7:
Immediate cracking of a weak password like “apple.”
Table 3:
Comparison of attack success rates based on password strength
| Password strength | Example password | Dictionary attack | Brute-force attack | Rainbow table attack | Estimated cracking time |
|---|---|---|---|---|---|
| Weak (common words, <8 characters) | password123 | Easily cracked | Very fast | Likely pre-computed | Seconds to minutes |
| Moderate (8–12 characters, mix of letters, and numbers) | Pass1234 | May not be on the list | Feasible | Slower due to partial unpredictability | Minutes to hours |
| Strong (>12 characters, mix of letters, numbers, and symbols) | G@7$#m!Xz29 | Highly unlikely | Requires extensive computation | Not found in pre-computed tables | Years to centuries |
| Very strong (>16 characters, randomly generated) | B^&hZ0sTq1*!93 | Not in dictionaries | Practically infeasible | Hash cannot be reversed easily | Centuries or more |
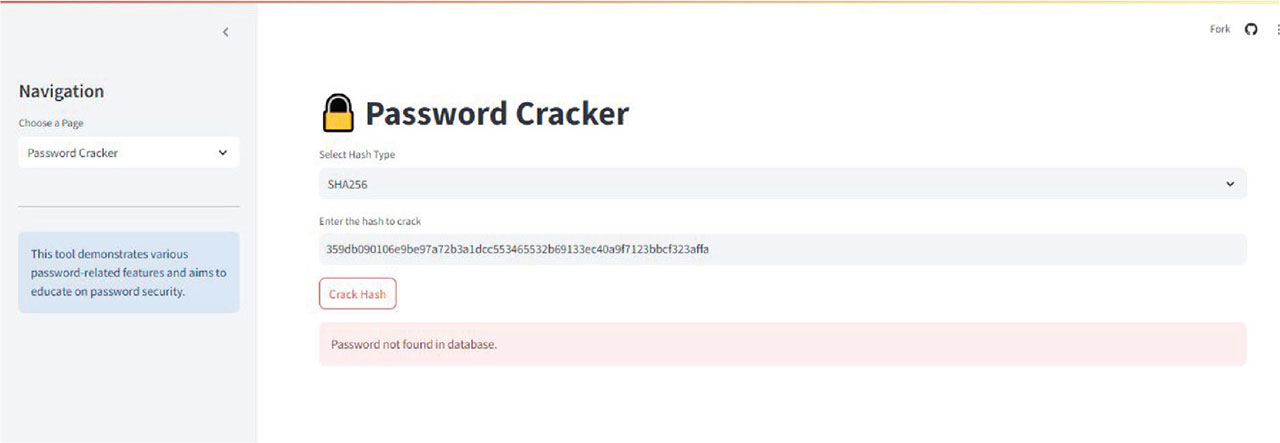
Figure 8:
Cracking hash of a strong password like “/)]N;PGFy!23”.
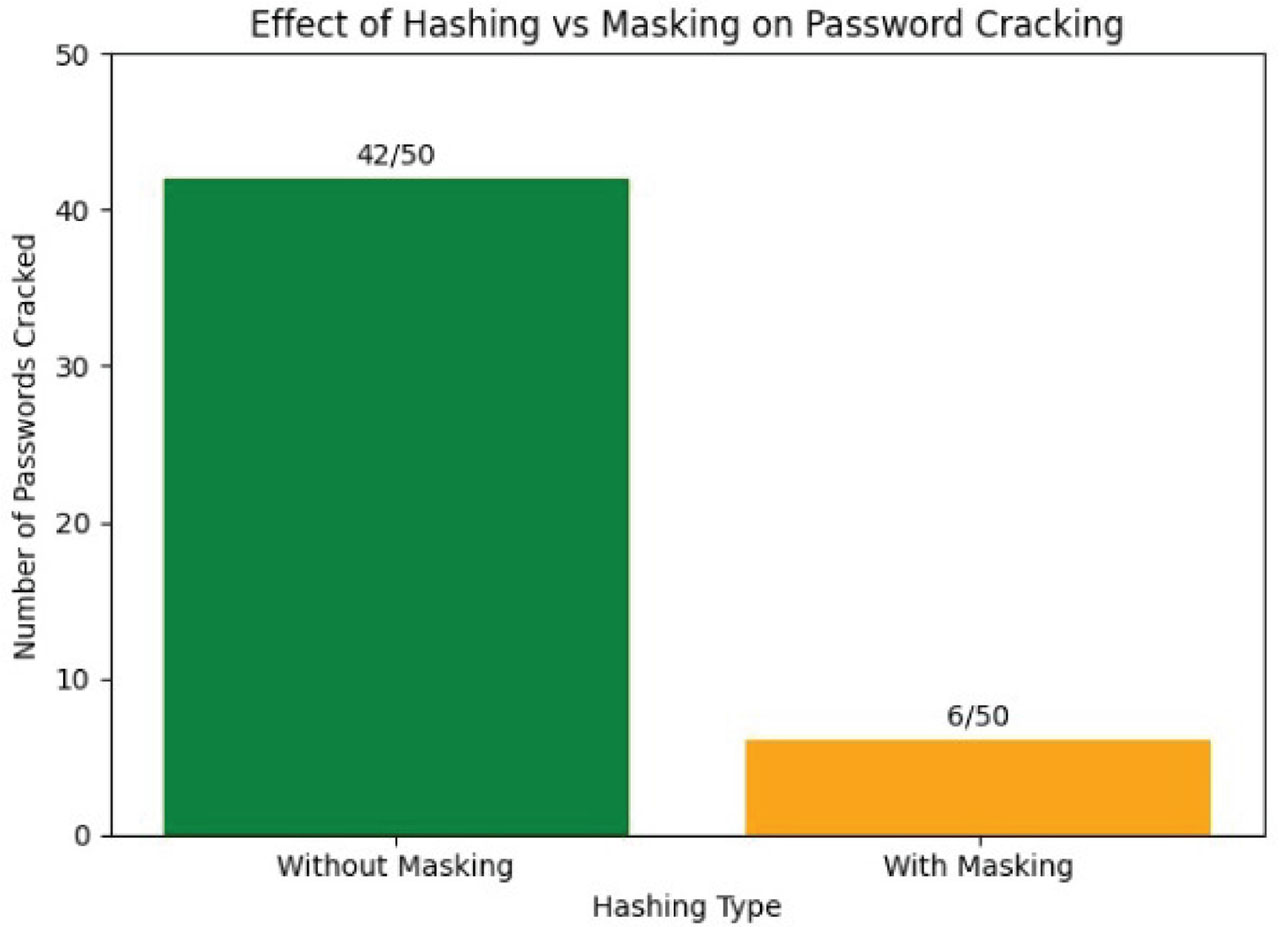
Figure 9:
Comparison of hashing versus masking on password cracking.
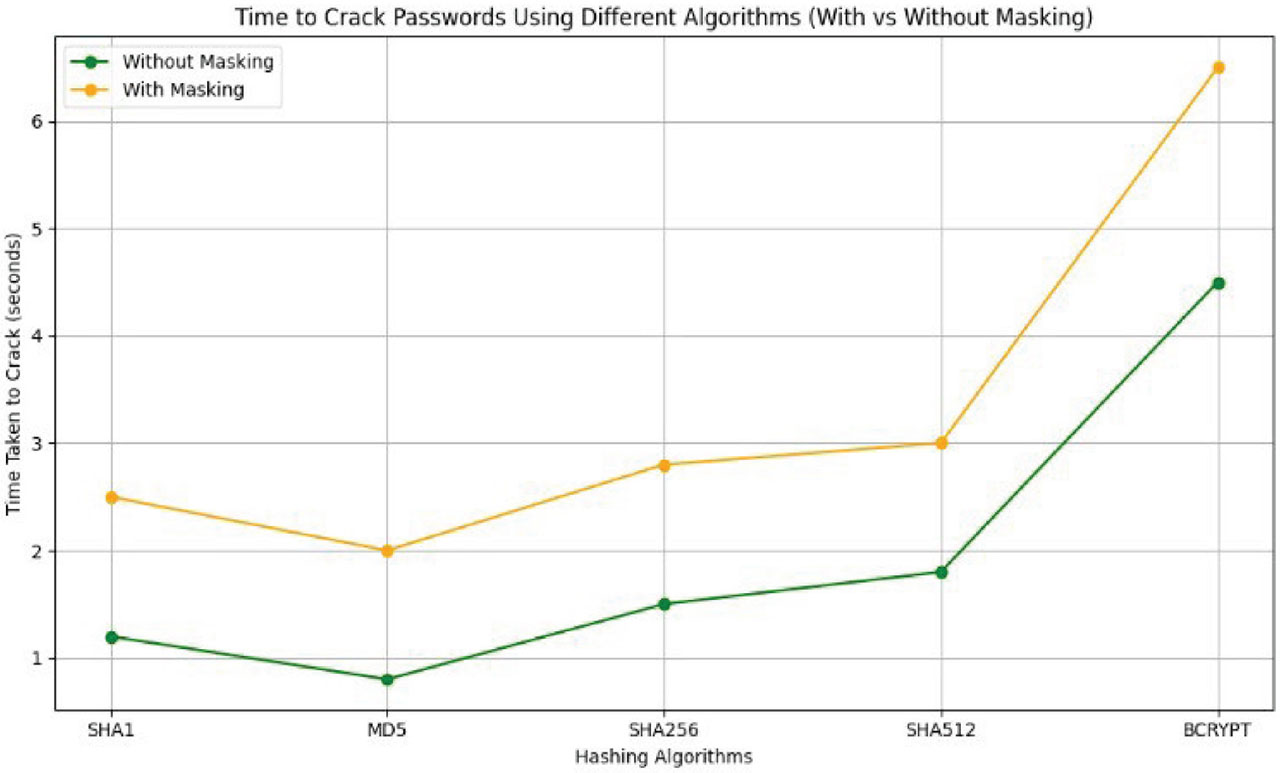
Figure 10:
Time comparison to crack passwords with various algorithms (with and without masking).
Table 4:
User engagement and password security insights
| Metric | Value | Insights |
|---|---|---|
| Total users engaged | >500 | Indicates strong interest in password security. |
| Average password length | 9.2 characters | Suggests most users create moderately strong passwords. |
| Weak passwords detected | 42% | A significant portion of users still use insecure passwords. |
| Moderate passwords detected | 35% | Users have some security awareness but room for improvement. |
| Moderate passwords detected | 35% | Users have some security awareness but room for improvement. |
| Strong passwords detected | 23% | Only a minority of users follow best practices for password security. |
| Most common attack success rate | 60% (dictionary attacks) | Highlights the widespread use of common or predictable passwords. |
| Average time to crack weak passwords | <1 min | Demonstrates how easily weak passwords can be exploited. |
| Average time to crack strong passwords | >10 years | Strong passwords remain highly resistant to attacks. |
| Most common hashing algorithm used | SHA-256 | Indicates the preferred standard among users. |
| User improvement after feedback | 30% improved passwords | Shows the educational impact of PassCrack recommendations. |